GDPR
Is your organisation GDPR compliant?
The GDPR or ‘General Data Protection Regulation’ (Regulation 2016/679/EU) is a new single EU law dealing with data protection that is intended to do away with the fragmented system that was previously in place and update laws across the EU that have not kept up with the digital age we live in. On 25 May 2018, as in the case of other EU Member States, the GDPR took effect in Malta. The new Data Protection Act, 2018 (Chapter 586 of the Laws of Malta) has also come into effect. Data controllers and processors had until this date to prepare for the various new, and in some cases, onerous obligations introduced by the GDPR.
Maltese organisations (especially those processing large amounts of personal data) must take all necessary measures to ensure full compliance with this new law and this, as soon as possible.
UNDERSTANDING GDPR
GDPR at a glance
- Fines up to €20,000,000 or 4% of an entity’s total worldwide annual turnover
- Significantly expanded territorial scope
- Mandatory data breach notification in certain cases
- Mandatory appointment of a Data Protection Officer in certain cases
- Data Processors now also directly responsible at law
- More stringent consent requirements
- Increased level of information to be provided to data subjects
- More stringent requirements in controller-processor contracts
- Removal of the general notification requirement
- New data subject rights
WHAT WE BELIEVE IN
How can we help?
Our Reputation
Mamo TCV Advocates is a leading Maltese law firm with years of experience in the field of privacy law and, in particular, data protection law. With clients ranging from world-famous multinational IT companies to individual data subjects we can provide your organisation practical advice regardless of the situation you are in.
GDPR Compliance
Over the past years we have carried out several GDPR audits and training sessions for our diverse portfolio of clients and we are now assisting clients with their various new obligations at law. From rules relating to direct marketing to data retention obligations, we have you covered.
What we Offer
- Comprehensive expert legal advisory services
- Data protection risk assessments
- Training of DPOs and other staff members
- Drafting of layered privacy policies & other notices
- Drafting of data processing agreements & addenda
- Full legal representation in contentious matters and/or IDPC investigations


Stay updated with our latest insights
EU Commission Classifies ChatGPT as a Search Engine: A Brief Look at What This Means
The European Commission has recently designated OpenAI’s ChatGPT as a Very Large Online Search Engine (“VLOSE”), whilst Roblox and Reddit have been designated as Very Large Online Platforms (“VLOPs”), making all three subject to the Digital Services Act (“DSA”) . Having each exceeded an average of 45 million monthly users throughout the European Union (“EU”), the newly designated services now have four months (until January 2027) to comply with all additional requirements mandated by the DSA for both VLOSEs and VLOPs. This is particularly noteworthy in the case of ChatGPT, which has now joined the two other VLOSEs, 'Bing' (operated…
Ian Deguara Joins Mamo TCV Advocates
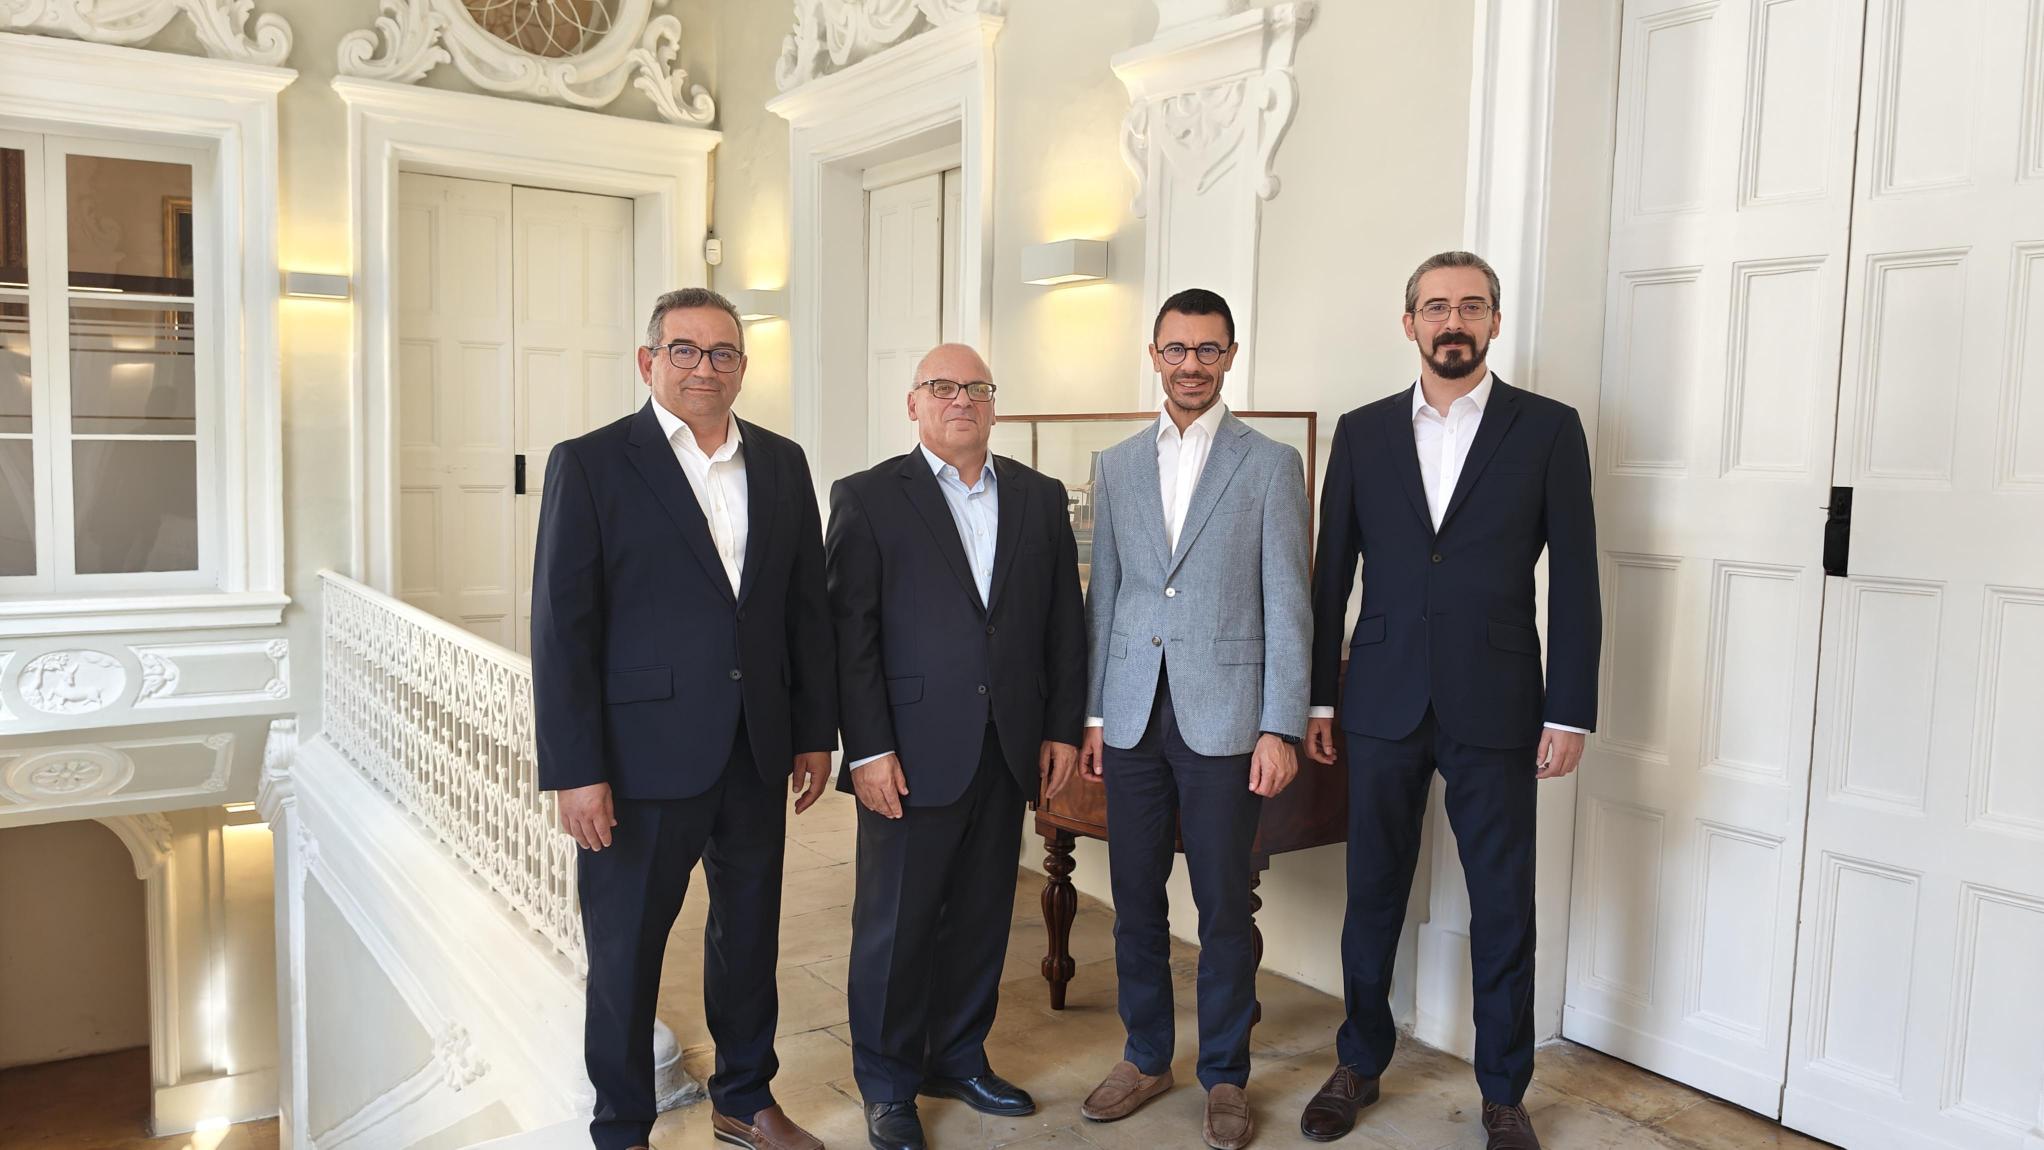
In August 2026, Mr Ian Deguara, the former Maltese Information and Data Protection Commissioner, joined Mamo TCV Advocates as Senior Regulatory Advisor. Mr Deguara’s term at the Office of the Information and Data Protection Commissioner (IDPC) came to an end in March 2026. Mamo TCV Advocates’ Managing Partner, Dr Joe Borg Bartolo, welcomed Mr Deguara to the firm, describing his appointment as an important milestone for both the firm and Mr Deguara as he begins this new chapter of his distinguished career in the field of privacy and data protection. Dr Claude Micallef Grimaud and Dr Antoine Camilleri, both partners heading the…
EU AI Act Update: What Will Apply From 2 August 2026 And What Is Being Postponed?
In a recent press release, the Council of the European Union announced that a provisional agreement on the Digital Omnibus Regulation on AI (hereinafter the “Omnibus”) was reached, introducing certain amendments to the EU AI Act (hereinafter the “Act”). Most notably, the provisional agreement revises the timeline for the applicability of certain provisions of the Act, particularly concerning the obligations applicable to high-risk AI systems. In this respect, the application of the obligations with respect to high-risk AI systems listed under Annex III of the Act would be postponed to 2 December 2027. For high-risk AI systems which are embedded…